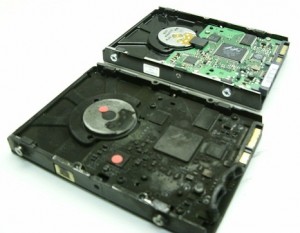
Almost every month someone in Canada sends a hard drive that has been involved in a house fire. They often resemble burnt bricks like the picture below of a drive we recently received from a client in London, Ontario. None of our techs were in a hurry to get their hands dirty, but as terrible as these situations look, there is often an easy recovery lurking just under the mess!
Plastic melts easily and this external hard drive is in-cased in plastic like a pair of jeans on a teenager in the 80’s.
But with a little invasive surgery we are able to free the hard drive from its prison.
But will the prisoner be able to talk?
As we have discussed various times in this blog, it is the condition of the disks that will ultimately decide if we can make this hard drive talk again. So let’s open the bonnet and have a peak under the hood …
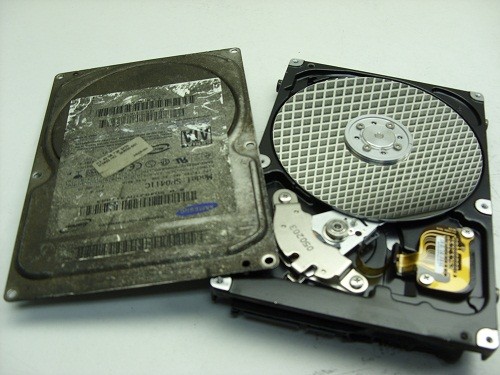
WOW! It looks pristine. Notice the lack of any contamination due to the fire or the liquids used to douse it. We proceeded to perform a full recovery on this case by replacing only the PCB
Below is another fire victim from a client in Montreal, Quebec which was not in such great shape when we opened the lid. In fact, it may not be recoverable … but we’ll never know for sure as the client declined our quote.
As a general rule for data recovery purposes, fire damaged drives are not typically unrecoverable due to the heat and smoke of the fire, BUT more often, it is the excessive use of firefighting liquids that do the damage, especially if they are allowed to dry out. The drying out leaves mineral and other debris deposits on the disks which are tough to overcome.
And here is a look of what happens when someone applies power to a fire damaged hard drive that has had the sealed assembly breached. You can see the deep ring on the inside of the disk where the heads are. This disk drive will NOT be recoverable.
So if you have a sad looking case of melted data don’t give up hope, data recovery may be as easy as a PCB replacement.
In my last blog I recounted how we managed to recover the data from a multiple hard drive RAID array AFTER two different European data recovery companies had failed. In that situation, we were the white knight, coming in to save the data where others had failed. But recently, we were painted as the villain for performing similar data recovery magic right here in Toronto. In fact, the title of this blog came from our 1st ever negative Google review as a result of this recent case.
To summarize, we received a 2.5” Western Digital WD hard drive for data recovery. The particular model drive sent in, has a USB3 interface built onto its PCB (printed circuit board) and it does not have typical SATA connections. From experience, we have found that data recovery imaging utilities (both in-house written and commercial) work terribly with USB interfaced hard drives. As a result, we don’t attempt to access or image USB3 type WD drives using their native USB PCB. Instead, we have learned how to convert a particular standard WD SATA PCB to work with these native USB drives.
So when we received this case, we immediately converted one of SATA PCBs to work with this drive. The conversion process required us to remove one small 8 pin programmable chip from the client’s original USB3 PCB and transfer it onto our SATA PCB. Once we did this, we were able to evaluate the drive fully and concluded that the drive had bad heads and likely minor disk damage. We contacted the client and quoted them $1300, which they declined. We transferred the client’s 8 pin chip back to their original PCB and returned the drive to the client.
The client then took it to another data recovery company who claimed it was unrecoverable because we had damaged the PCB and furthermore we left solder paste around the 8 pin chip and were thus “VERY AMATEURISH”. Ok we forgot some totally inconsequential solder paste on the PCB. But we never once applied power to the PCB so the claim we damaged it seemed unfounded. Of course there was a chance we damaged the small 8 pin chip so we suggested the client bring it back to us. They did; we removed the chip and verified it’s functionality using a chip reader. While it was here, we re-established the fact that we could still recover the data, but again the client did not want to pay us anything and left with their drive intact but with no solder paste residue to complain about.
Apparently, the client then went to KROLL ONTRACK, “the industry leader and the largest data recovery provider in Canada and in the world”. The client claims they also declared the drive unrecoverable due to the same “damaged” PCB.
The client then came back to us, and we again re-iterated that we had not damaged anything, and we could still recover the data for him. In fact, just to keep our good guy image alive, we offered to reduce the cost by $300. At 1st the client accepted thinking we offered the recovery at $300. But when he realized we weren’t giving it away and still required $1000 to complete the recovery he declined and created his mean spirited Google complaint.
Whether this client was trying to get a free recovery or not, I don’t know, or care, but in the end I am aghast that 2 other professional data recovery companies in Toronto cannot recover the data from a situation where we regularly do.
It helps to realize, that the world wide data recovery industry has no standards, no way of knowing a company’s competency, or a company’s integrity. There are lots of bad guys waiting to take your money for very little in return and many posers issuing inaccurate statements about what is recoverable and what is not. The damage they can cause is inexcusable. I have heard it said that something like 70% of small companies that lose their data permanently are out of business within 6 months. Don’t be one of them!
If your data is important, don’t believe the 1st “It’s UNRECOVERABLE” that you hear. Data recovery companies and technicians are not created equal. Please seek a 2nd or 3rd or 4th opinion, or maybe you should just come to Memofix Data Recovery Services first.
As a member of a worldwide consortium called the TSC or Technical Services Consortium, we are part of a family of companies that offer many of the same services, but in different geographical areas. Because we are not competing with each other, we have developed some amazing business relationships with folks that would normally be our competitors. This has allowed us to gain knowledge in areas where we were weak and to share knowledge where we are strong. As the only member of the consortium offering data recovery services, we often get called in to help with data loss situations.
Recently one of our TSC partners in the Netherlands, Sprague Europe, was approached by a well-known University in Germany. The University had had a catastrophic failure with a small RAID 5 server and the hard work of hundreds of students was in jeopardy.
Initially the University had contacted a well-respected but smaller data recovery company in the Netherlands to help. They were able to image one of the 3 drives used in the RAID 5 array, but unfortunately, all attempts at resurrecting either of the remaining two drives was met with failure.
With RAID 5 and it’s built in redundancy, we only needed to image one of the two non-responsive drives to be able to rebuild the RAID. Both drives had developed light rings on their disks and the heads were physically destroyed by travelling over the damaged areas and had become stuck in the head loader ramps. With each recovery attempt, these rings would increase in depth and width, and soon no recovery would be possible. The smaller Dutch data recovery company had exhausted their supply of parts drives and realizing the chances for success were decreasing with each attempt, they advised the University to send it to Kroll Ontrack, the largest data recovery company in the world. Ontrack had a branch in Germany and off the case went.
But again, all attempts to recover the data were met with failure and the University was almost ready to concede defeat. But as luck would have it, the head of the University’s Computer Centre was an old colleague with one of our friends at Sprague and in a last ditch effort he called Sprague for advice. Our friend at Sprague suggested Memofix “may” be able to help.
Unlike most data recovery service providers, Memofix does not charge an extra fee for working on hard drives that have been previously worked on by other data recovery companies. In fact we cherish those data recovery cases because it gives us a chance to show just how good we are. Over the years we have recovered approximately 70% of the recoveries that have been previously attempted by our competitors.
When I first saw the request and the summary of what had been attempted, I was skeptical if we could do any better than the two professional data recovery companies that had already tried, especially when one of them was a “world leader” in data recovery and cost did not appear to be a constraint. I spoke with the original data recovery company that tried the 1st attempts. They told me that both defective drives had heads that were bent, distorted, and stuck in the head ramp loaders. They also told me that they had gotten both defective hard drives to function for a very short period of time after replacing the head assembly. Things were looking a little more promising.
When it comes to recovering data, there is one MAJOR factor that influences the chance of recovering data and that is the condition of the disks. If the disks are in good shape, a recovery is usually going to be possible. If the disks are badly scored and ringed, then it will be next to impossible to get a set of heads to function inside the drive without damaging them almost instantaneously. For a disk to get that badly damaged usually means the drive has been running/spinning in a crashed state for a long time. The fact that these drives had their heads stuck in the loading ramps is good news, as they could no longer damage the disks. The second fact that made us hopeful was that the drives were manufactured by Western Digital and Memofix has one of the best Western Digital data recovery techs that we have ever met and we do know a lot of data recovery techs.
So we decided that we may have a chance of successfully recovering at least some of the data and consequently the case was sent to us for a final data recovery attempt.
Our initial evaluation confirmed that we would need to get one of two defective drives imaged. After much scrutiny it was determined that one of the defective drives had shifted disks. When heads are replaced, there is a procedure for adjusting the disks which can sometimes help in getting access to a non-responsive hard drive. I suspect one of the data recovery service providers had attempted this procedure or something similar. This procedure can sometimes make things worse, so we decided to concentrate on the more pristine of the two drives.
Our Western Digital data recovery specialist got right to work. His first task was to get the drive functional enough to read off the drives system area, a normally inaccessible storage area on the drive used for its own housekeeping and the storing of drive specific settings. The system area tells the drive how many heads are present and what settings to use with each head. Without this road-map, recovery may not be possible.
Bent Heads vs Good Heads
We quickly determined that two of the disk surfaces had physical damage and we would worry about those surfaces last. Modifying the system area allowed us to configure the drive to ignore the 2 damaged heads/surfaces. We then physically removed the 2 heads (corresponding to the damaged surfaces) from a good parts head stack. This would prevent further damage to those disk surfaces as well as preventing read interference from the heads going over the damaged areas. We then used this head assembly to get the drive to initialize and we started to image off the good surfaces. After approximately 20 hours of imaging, the heads assembly became too contaminated with crash debris to function and we had to modify a new set of heads to continue. After two days we had managed to image 6 of the 8 disk surfaces. We were now ready to go after the two damaged disk surfaces.
At this stage, our greatest danger was the inherent risk of developing new crashes & destroying our chances of imaging off the last two disk surfaces. Consequently, the drive was imaged only while it could be monitored by a dedicated human watching and listening for any potential new crashes. Imaging of these last two surfaces took almost a week and in the process we consumed five sets of heads and still had some areas where nothing could be read because of the damage to the hard drives’ disks.
With the best drive images we could obtain, we began to analyze what we had. Once we determined the correct RAID 5 configuration settings we were able to use the RAID’s parity to virtually rebuild the missing disk and to de-stripe the 3 drive RAID 5 volume onto a single drive. Then it was a matter of repairing some minor file system structure damage, mounting up the volume, and copying the data to a new target hard drive.
In the end, we were able to recover over 99% of all the students’ data. But there wouldn’t have been any data recovery had it not been for one individual at the University refusing to take NO for an answer.
Consequently, I think the real takeaway point, has to be the fact that not all data recovery companies have the same abilities and just because the world’s largest data recovery company says it can’t be done, doesn’t mean Memofix, the world’s most determined data recovery company, can’t prove them wrong.
If you’ve ever been the victim of a house fire, you understand what a mess it can create. But interestingly enough, a lot of the mess can be attributed to the actions used to extinguish the fire, versus the fire itself. In particular, the spraying of water and other firefighting liquids can create a wet soggy environment which is definitely not friendly for electronic devices such as your computer or the hard disk drive that resides inside.
Recovering data from hard drives which have been exposed to heat, fire, and water is not as exponentially difficult as some data recovery companies may lead you to believe. Even a hard drive as badly burnt as the one below was a fairly easy recovery for our skilled data recovery technicians located in Toronto. Notice the difference in color due to the soot and smoke, as well as the melted PCB and plastic connectors.
Will my data be recoverable after a fire?
But what really determines if the data will be recoverable or not? We can replace melted PCBs. We can replace damaged head assemblies. We can rebuild missing NVRAM data. But it is the condition of the disks or platters that are most important when determining the chances of successfully recovering the data on any damaged hard drive. In most of the fire cases we see, the hard drive’s pressure equalization valve and lid seal are successful in protecting the disks from exposure to the fire or fire retardant liquids. In those where the seal was penetrated we may find some water residue which can usually be cleaned successfully.
And when we open this fire burned drive, we see a pristine gleaming disk with no apparent water, soot, or other residues being present. And as is typical with most house fires the heat was not severe enough to warp or bend the disk(s) in anyway. So once we replaced or rebuild the damaged components we were able to get the hard drive functioning long enough to create a sector by sector image of the hard disk drive. We then successfully recovered all the client’s files from this image.
Inside a fire burned or well done hard drive.
Not all recoveries are as simple as this burn victim, but our extensive expertise allows us to successfully recover data from over 90% of the burned hard drives we receive for data recovery. If your hard drive is the victim of fire and you need your data recovered, we would recommend that you seal the disk drive in a zip lock baggie as soon after the fire as possible. This will prevent any water residues from evaporating and leaving mineral deposits on the disk surfaces which may hamper our recovery attempts. And remember, even if things look grim, we can often put a smile back on your face. www.memofixdatarecovery.com
In my last post we discussed the consequences of formatting your hard disk drive using Windows XP, Windows Vista or Windows 7 and whether data could be recovered after such an event. In this post we will shed some light on how Apple implements formatting on the MAC, and the implications of their methods on data recovery.
First it should be noted that Apple does not use the standard Windows terminology when referring to formatting a hard disc drive. Apple calls their format process “Erase”, but in essence it perform the same tasks as a Windows Format command. The hard drive is re-initialized to appear as a fresh and empty drive volume with all of the disk space free for use.
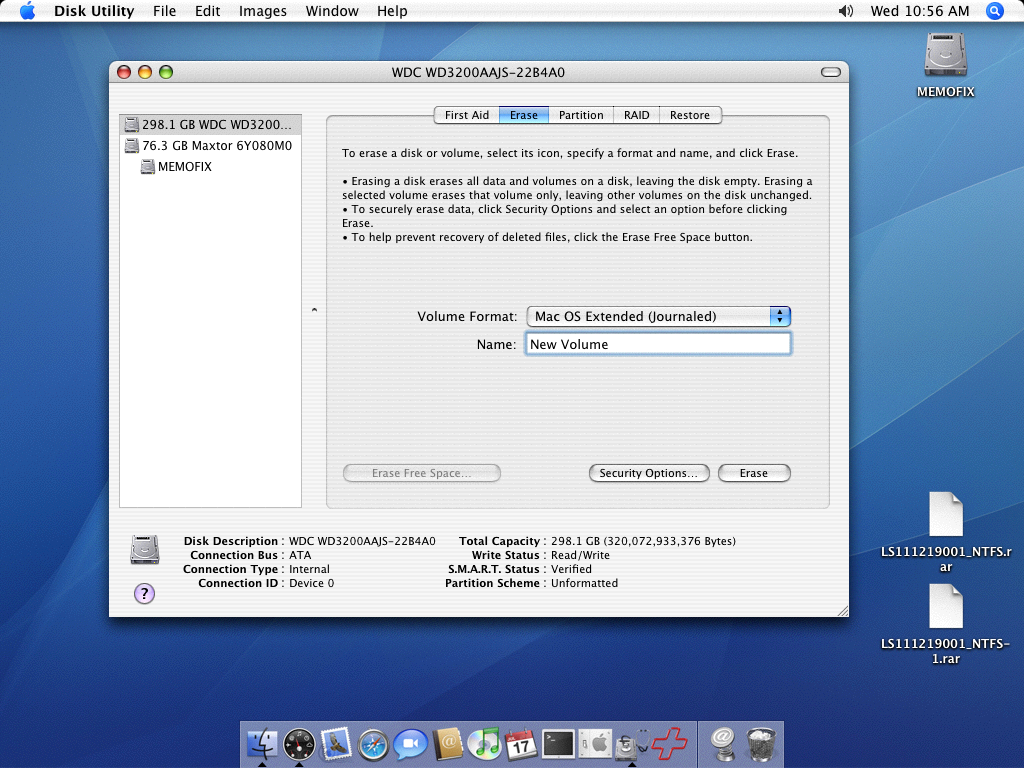
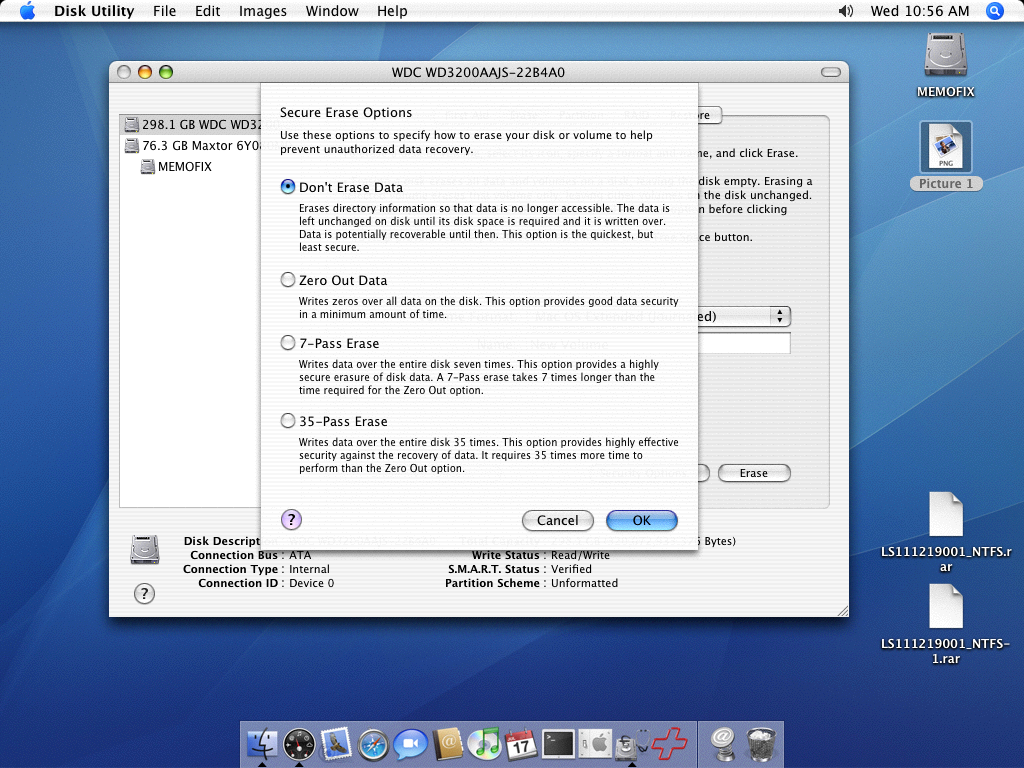
Mac’s Disk Utility can be invoked from the “Go-> Utilities” tab. A screen shot of the disk utility can be seen below. When a hard drive is selected you can then choose the type of Volume Format and a name for the new drive volume.
If you were to now press the Erase button, the drive would be formatted or erased according to the Security Options that are set. To see what options are selected, press the Security Options button and you will see the screen shot below.
By default, an Erase is set to the “Don’t Erase Data” option. This option overwrites all the directory information used to find and access a file. It does not however erase the actual data. In this case, data recovery should be possible. This option is equivalent to a quick format on a Windows based PC.
The use of any of the other options will result in permanent data loss. Whether you overwrite the data 1 time, 7 times or even 35 times makes no difference in the real world of data recovery. The data will be gone, so be careful.
Enterprise level RAID arrays often use SCSI or SAS (serial attached SCSI) hard disk drives. Compared to PATA and SATA IDE hard drives, SCSI and SAS are not as common. And as a result few data recovery companies have much experience with them.
Fortunately, Memofix (located in Vaughan, Ontario) has been around for so long that we still remember when all servers and RAID arrays used SCSI hard drives. I too have been “around” for a long time and during my 12 years at ActionFront and Seagate Recovery Services I was the “go to guy” for SCSI recoveries. By the end of my career at these Toronto GTA based recovery companies, I was full-time management with the exception of working exclusively on cases that used SCSI hard drives. As a result, I became thee expert at resurrecting dead SCSI and SAS drives. And as they were most often used in RAID arrays, my skills at rebuilding and recovering RAID data was also very good.
At Memofix this expertise has been passed on, but I still personally monitor every SCSI, SAS and RAID array we receive. I believe we are the best in the industry whether that RAID is used on a MAC. Windows, Unix or even a Solaris operating system. If you need some expertise on your failing RAID call the professionals. http://www.memofixdatarecovery.com/data-recovery-raid.php
To most of us, the word “encryption” conjures up images of spies and secret disks containing information that must be guarded at all costs. Few of us realize that we all rely on and use encryption almost every day in our normal lives. Whether making a cell call, sending an email, buying something with your debit card, or accessing the web wirelessly, we are using and being protected by this not so simple process.
What is encryption? Encryption is the process used to transform and disguise data so that it is unreadable or undecipherable to anyone without a pre-determined secret code or password. Basically, the data to be encrypted is sent through an elaborate algorithm using the secret code or password to scramble the data into indistinguishable rubbish.
Please note, that password protection is NOT encryption. Password protection “may” prevent access to the data, but it does not alter the actual data. Password protection can be easily bypassed.
Encryption has also become common place for protecting data on computer based storage device like hard drives and USB flash sticks. Encryption can be used to protect an entire volume, a folder or even a single file. There are several distinct implementations available:
SOFTWARE, Users can buy or use free encryption programs that make it possible to encrypt files, folders or even their entire hard drive or flash device using software routines to intercept and modify the data on the fly. The entire encrypting and decrypting process is handled by your computer’s CPU or processor. Popular examples include SafeGuard, SecureDoc, PGP, TrueCrypt and Safeboot. Starting with XP Professional, Microsoft includes a built in folder and file encryption feature called Encrypting File System or EFS for short. Software encryption methods are popular as they are inexpensive and can be implemented on any existing storage device. However, they are generally much slower, typically 20% slower than hardware based methods.
HARDWARE, There are external hard drive devices that use a standard hard drive connected through a “hardware based” encryption interface board. In many cases this encryption process is performed without the user even being aware. Many Western Digital external boxes use this method allowing 100% data protection if the drive is ever removed from the enclosure and its encrypting interface board. Hardware techniques are considerably faster than software methods.
SELF ENCRYPTING, Users can now buy hard drives and SSDs that utilize on-board hardware to encrypt and decrypt the data on the fly. These devices encrypt the entire contents of a storage device and are referred to as SEDs or self-encrypting devices or drives. These drives carry a premium price tag but are the ultimate in safety and speed. Some hard drive manufactures such as Seagate may also refer to this self-encrypting as FDE or Fixed Disk Encryption.
Why use encryption? Most of us have heard a story or two about personal financial data falling into the wrong hands due to a corporate laptop being stolen or lost. Or the often recreated news story about reporters picking computers out of the trash and finding “valuable” info left abandoned. Yes it does happen, as someone who regularly buys previously used hard drives can attest. But just how many of us actually have super sensitive data on our computers in the first place? If you are one of the few that must keep your data from prying eyes, then by all means encrypt away. But if you don’t need to … DON’T!
Besides the potential loss in performance, there are several other reasons not to use encryption.
LOSS OF PASSWORD OR KEYFILE: If you can’t remember the password or can’t find the keyfile you made 3 years ago, you will NOT get your data back, period. While there are numerous recovery techniques for decrypting or accessing encrypted volumes, they all require some form of a username/password combo or a special key file created by the encryption software.
OPERATING SYSTEM FAILURE: If an encrypted drive’s operating system becomes corrupted, perhaps due to a simple virus and the drive is no longer bootable or accessible, there is no easy way to repair the file system and regain access. To resolve the issue you must first decrypt the entire volume. Again you will need a user/password or keyfile (and specialized programs) to perform such an operation. Once the volume is decrypted, the file system damage can then be repaired using the file system’s own repair utilities, i.e. chkdsk.exe
READ ERRORS: Over time storage device can easily develop read errors and if these read errors affect the operating system files or an area used to store pertinent encryption parameters, it can become impossible to access your data. As above, complicated procedures will be required to decrypt the volume and access the data. A single read error can stop everything.
Is encryption breakable? Theoretically, with enough computing power and enough time, any encryption scheme can be broken. But if the process takes a thousand years, the value of the data may be very limited. And fortunately the increase in computing power to break the key is easily outstripped by the exponential increase in difficulty by adding an additional bit to the encryption key. Presently, most credit card companies recommend transactions using 128 bit encryption keys. 128 bits keys are considered by the experts to be safe until about 2030 although some recommend 256 bit keys due to the advent of the “quantum computer” where theoretically the difficulty may be halved.
There are 2 basic ways of breaking encryption. The hacker either breaks the password by guessing the password or the hacker uses crypto analysis to guess the message based on the natural frequency and composition of the characters in a given language. To guess a password is often very easy as people tend to use real words and they are often chosen from an individual’s personal life or interests. Even brute force using a pre-created word list is often successful. To be sure your password can’t be compromised in your lifetime it has been recommended that your password should be at least 20 random characters. Of course few of us can remember such a long sequence.
In the real world, getting around the encryption is often much easier than either of these methods. Keyboard recorders are simple to install devices that can be used to record all the keystrokes of a user including their passwords. Or perhaps a hidden camera could provide the same results. Another technique can be utilized if a user leaves their computer unattended, as the contents of RAM memory are not encrypted and there are ways to dump the RAM contents and retrieve a password. Additionally, a group of researchers/hackers recently discovered that the contents of RAM memory do not disappear as soon as the power is removed. In fact if the RAM chips can be kept cool, the data may be retained for 10 minutes or longer. Theoretically reading the RAM contents could be possible even if the power is turned off. But this isn’t really so much about breaking the password as it is about stealing the password.
Can Memofix recover your encrypted data? Usually YES, but we need your keyfile or username/password combo … PERIOD. If we could recover your encrypted data without these credentials then what would be the point of using encryption in the first place.
We regularly recover data encrypted with PPG, Safeboot, SafeGuard, SecureDoc, EFS and most other software encryption programs. We are also very successful recovering hardware encrypted hard drives where the encryption is performed by an interface board separate from the storage device. i.e. the popular Western Digital My Book.
However, SEDs or Self Encrypting Devices present a real problem. It is estimated that by 2017 over 80% of all hard drives and all SSD or Solid State Drives will be SED or self-encrypting devices. There are NO decryption methods available for these SEDs and if consumers and businesses are to adopt these new SEDs, this concern must be addressed by the manufacturers.
Encryption is here to stay whether you need it or not. If you do choose to encrypt your data, we suggest you always create a key file and store it in a secure location. Additionally, record all usernames and passwords in a secure location and until the SED manufactures create a solution for authorized decrypting, we suggest you steer clear of their products or be sure to regularly backup.
As always, when things don’t quite go as planned remember your friends at Memofix https://www.memofixdatarecovery.com/ are always willing to help!